
From a flow record to a blocked IP address
Deep traffic analysis, threat detection, mitigation and regulatory support over a single data set.
Six areas on one dataset
DDoS protection
The system recognises an attack and stops it at your upstream peer via RTBH or FlowSpec – before it fills your uplink. Learn more →
Flow monitoring, RPKI and ASN
Every flow with its reputation, owner and path. 140,315 ASNs, RPKI validation and prefix hijack detection. Learn more →
NIS2 incident reporting
A guide based on the Czech Act No. 264/2025: your regime, the deadlines and pre-filled reports. Learn more →
Vulnerabilities and threat sources
Active and passive scanning, CVEs enriched with EPSS and KEV, and reputation from eight threat feeds. You know what to fix first. Learn more →
Data retention
Traffic data on a server in your own network. The data never leaves the rack. Learn more →
AI Audit and AI Shield
Which AI tools the company uses, where the data goes and how it could be attacked. Audit from CZK 29,000, continuous monitoring from March 2027. Learn more →
What you will not get elsewhere in one package
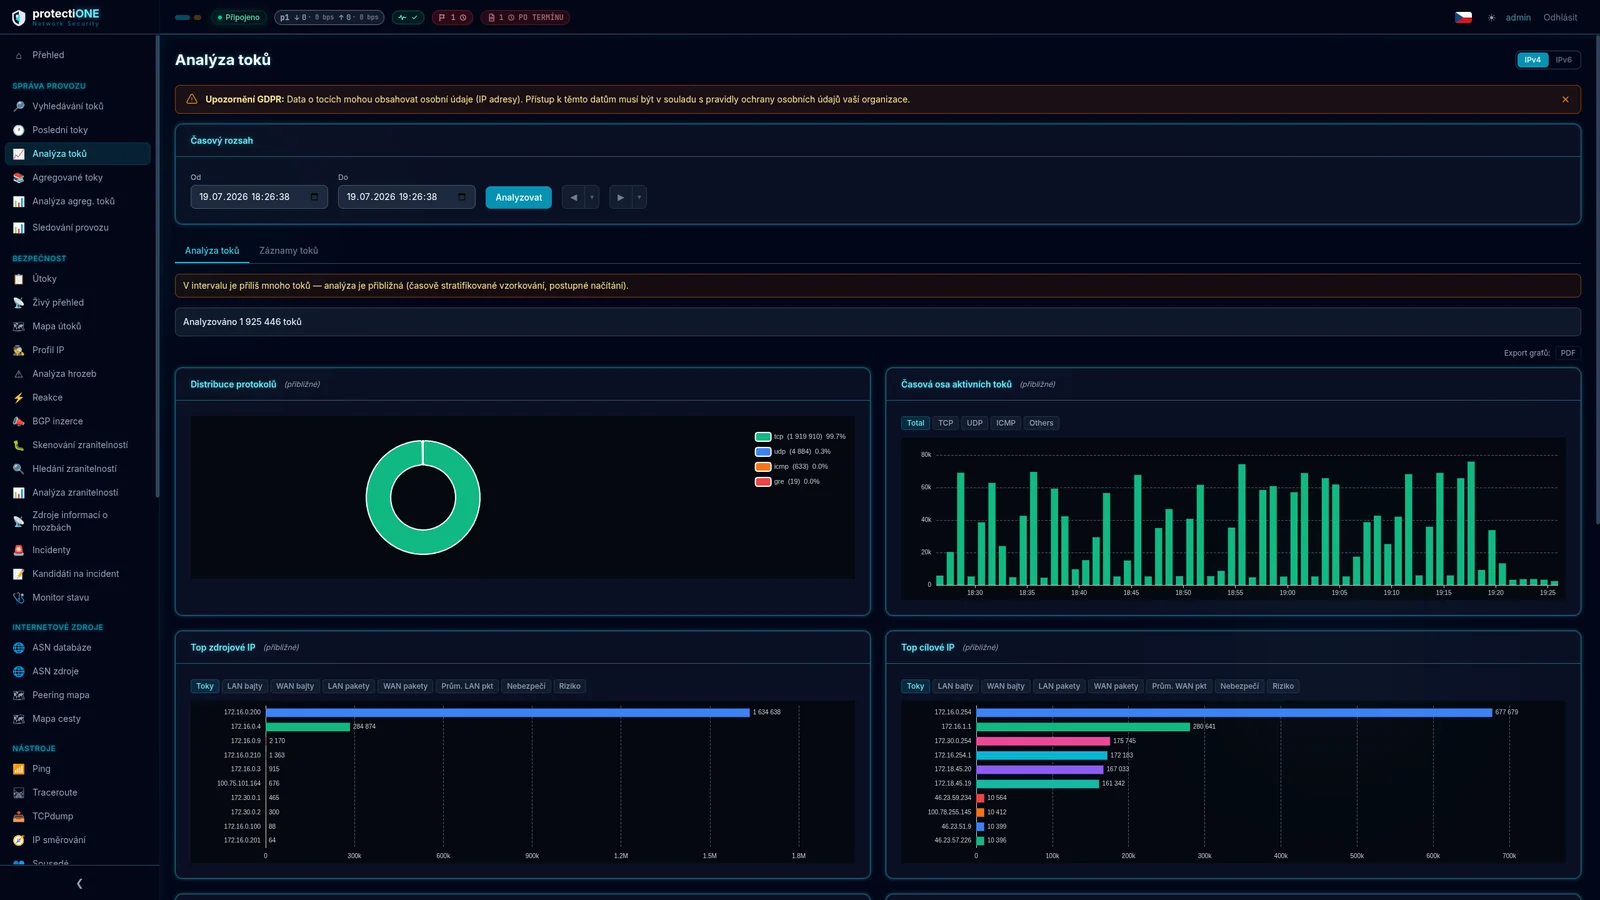
Deep flow inspection
Every IP flow analysed in real time.
Deep flow inspection
Every IP flow analysed in real time.
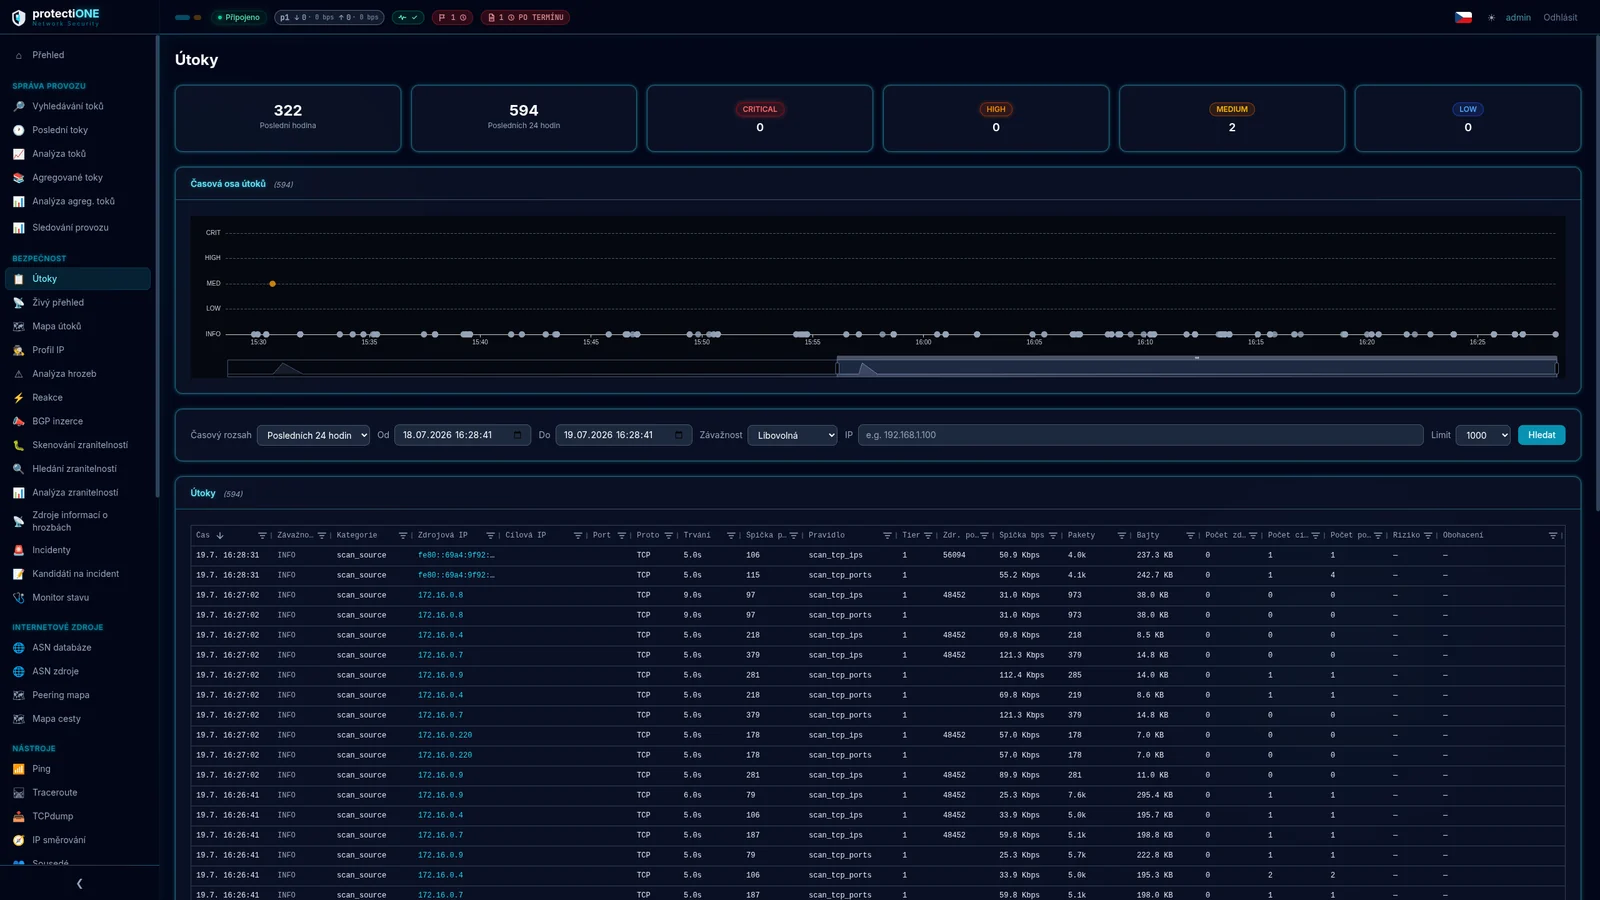
Automated threat detection
22 predefined rules in three families: floods against your addresses, floods from one of your hosts…
Automated threat detection
22 predefined rules in three families: floods against your addresses, floods from one of your hosts…
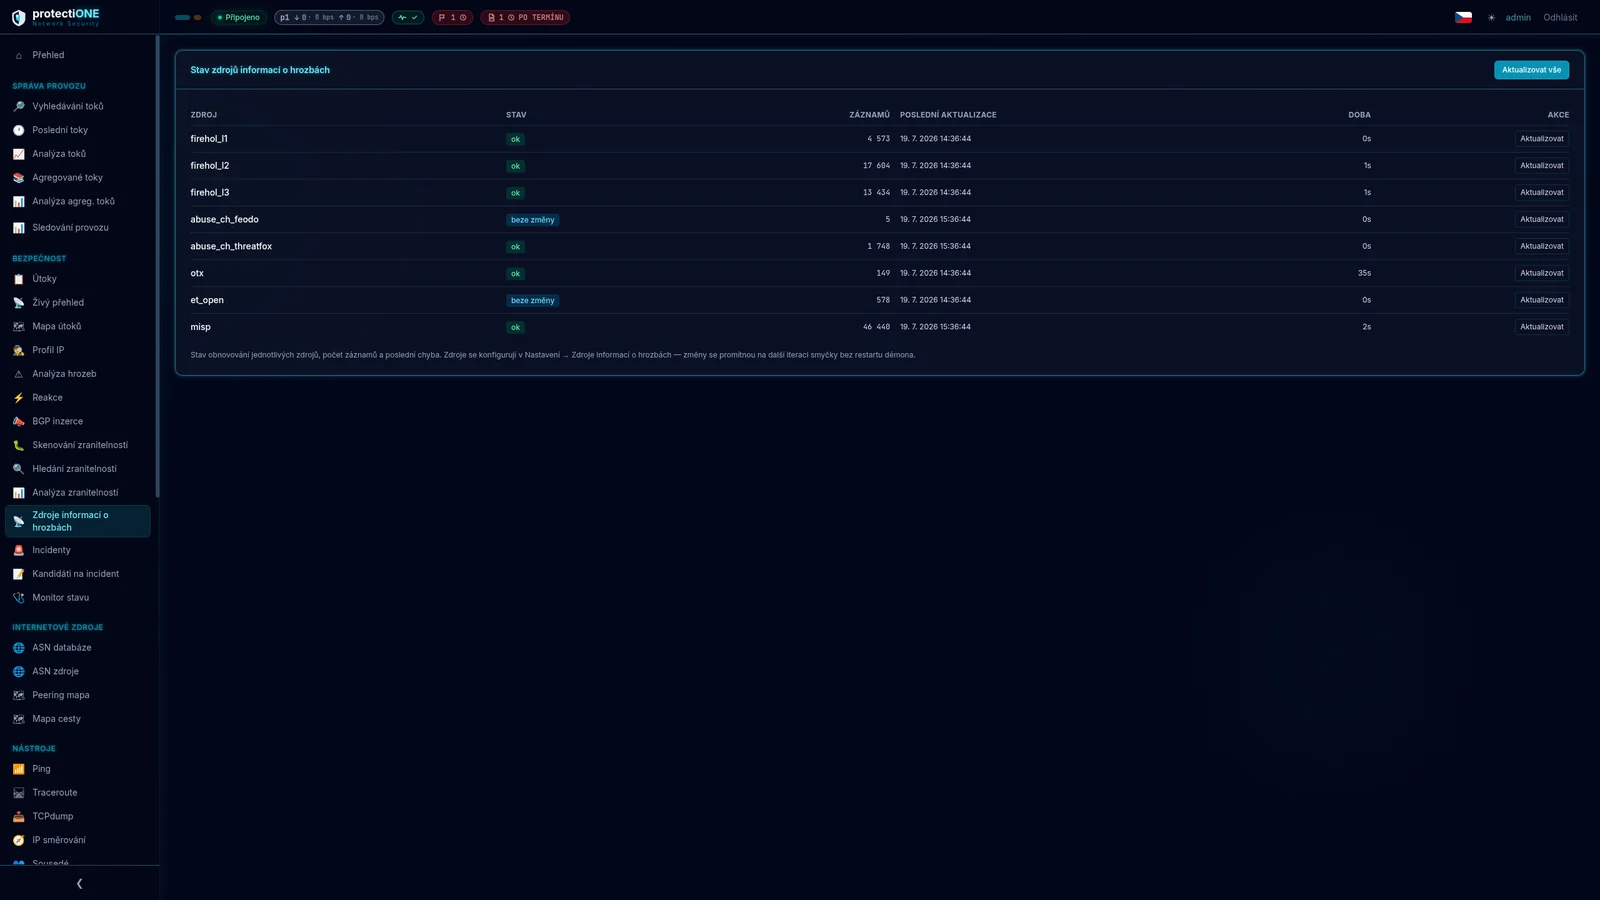
Context from global threat sources
Every flow is enriched with source reputation from eight feeds — FireHOL, abuse.ch Feodo and ThreatFox…
Context from global threat sources
Every flow is enriched with source reputation from eight feeds — FireHOL, abuse.ch Feodo and ThreatFox…
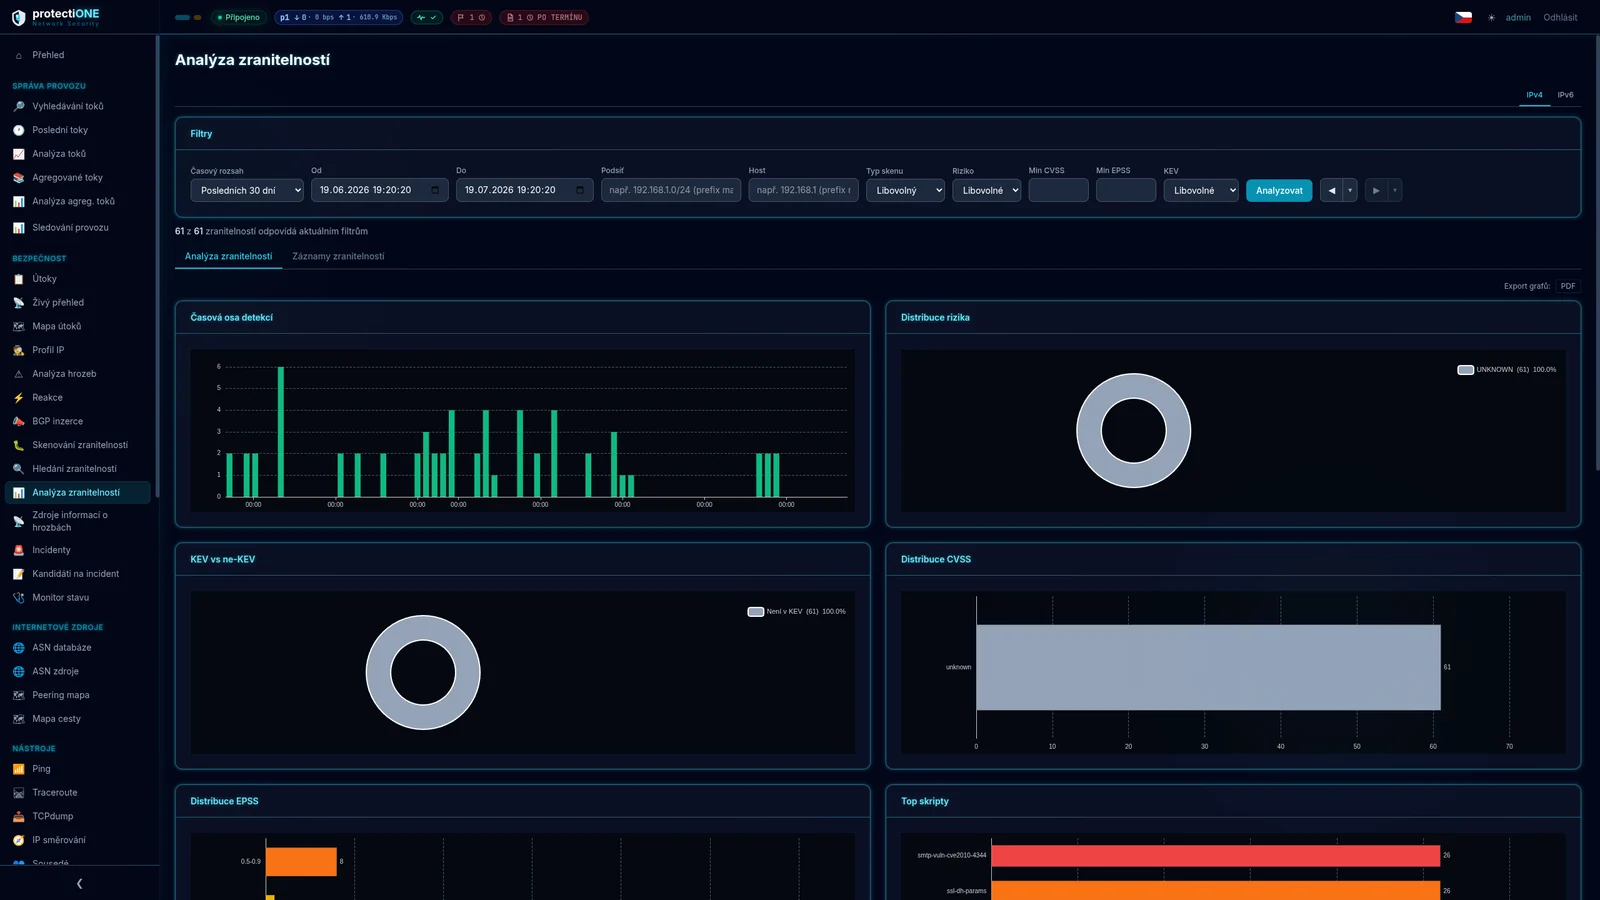
Vulnerability analysis
Vulnerability analysis
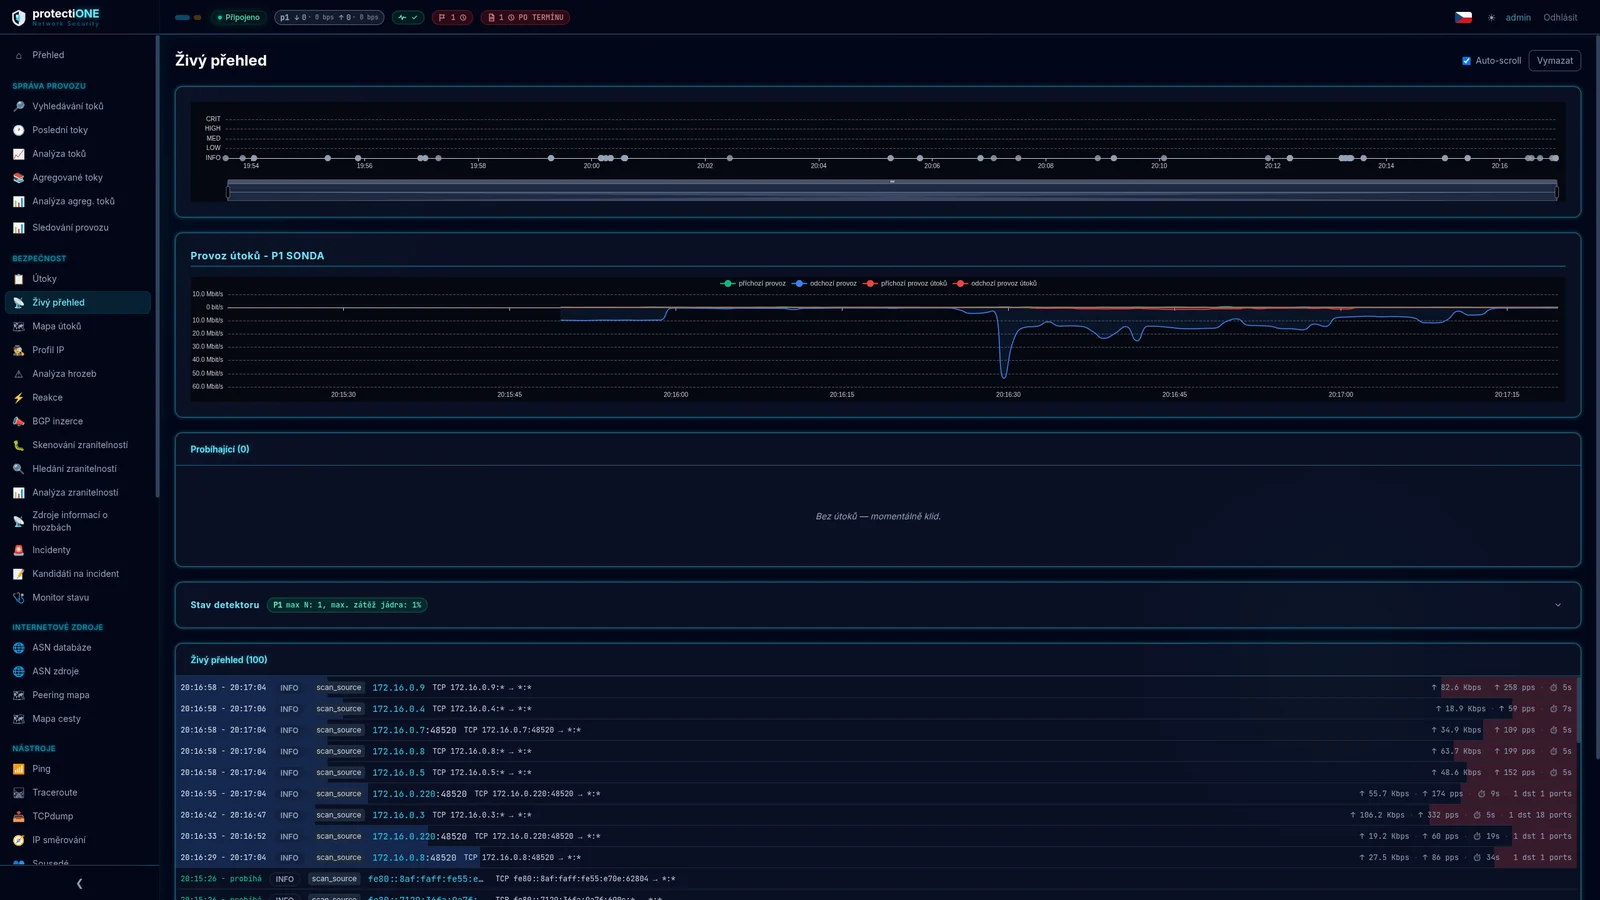
From an alert to an answer you can evidence
Every detected attack can be taken apart in depth — by its identifier, or by examining…
From an alert to an answer you can evidence
Every detected attack can be taken apart in depth — by its identifier, or by examining…
- Traffic Patterns — patterns that recur in your traffic
- Incident Simulation — rehearse how a response plays out before a real one arrives
- Stored forensic analyses with export
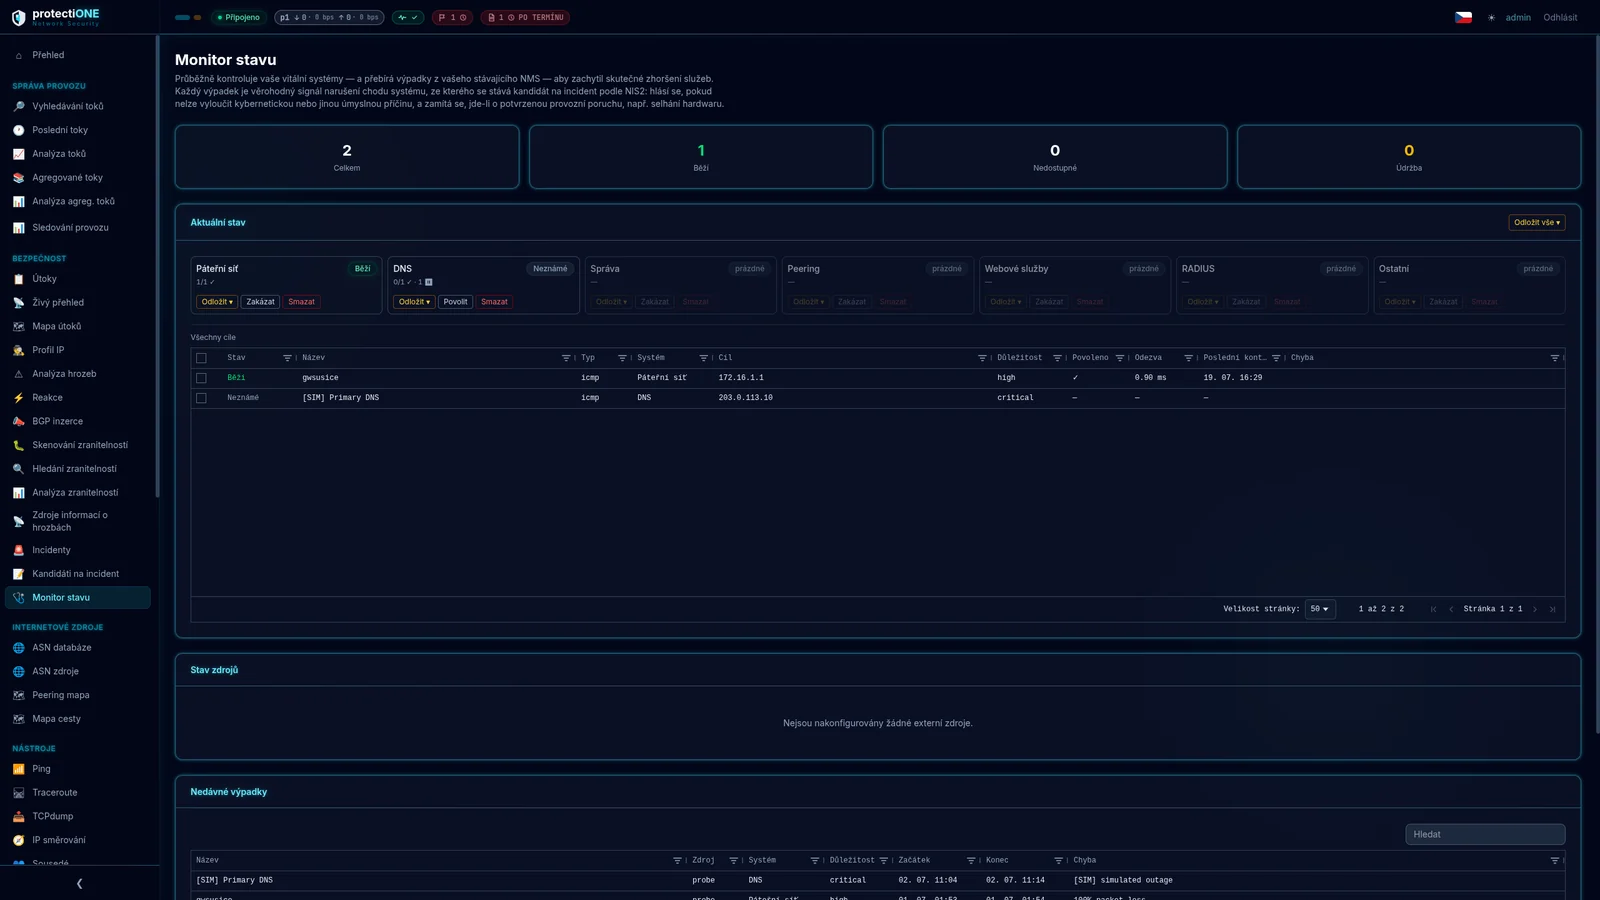
Traceroute where you see the flows
When you are handling an incident at three in the morning, you are not jumping between…
Traceroute where you see the flows
When you are handling an incident at three in the morning, you are not jumping between…
- Ping, traceroute, tcpdump and the routing table built in
- Neighbours, SFP module status, disks and database health
- SMART and IPMI sensors
Protectione vs. conventional NetFlow vs. SIEM
| Capability | Protectione | Conventional NetFlow | SIEM |
|---|---|---|---|
| Flow monitoring | ✓ | ✓ | ~ |
| Data retention | ✓ | ~ | ✕ |
| Threat intelligence | ✓ | ✕ | ✓ |
| Vulnerability management | ✓ | ✕ | ~ |
| Mitigation via RTBH / FlowSpec | ✓ | ✕ | ✕ |
| NIS2 to national law | ✓ | ✕ | ~ |
| RPKI and ASN intelligence | ✓ | ✕ | ✕ |
| ISP specialisation | ✓ | ~ | ✕ |
| Single platform | ✓ | ✕ | ✕ |
NIS2
The Czech Act No. 264/2025 has applied since 1 November 2025 and covers thousands of organisations – internet providers, companies and public bodies. Here is, in plain terms, who it applies to, what it asks and how Protectione guides you through it. Learn more →
DDoS protection
The system recognises an attack, names it and can stop it before it fills your link – via RTBH or FlowSpec at your upstream peer. Learn more →
Flow monitoring
Collection from NetFlow v9, IPFIX and port mirroring, with context from the ASN database and global threat sources. All on the same data, on one screen. Learn more →
Technical solution
The same platform, the same features, the same dashboard. All that differs is where the system runs and who owns the hardware. Learn more →
Pricing and SLA
A subscription sized to your network, hardware sized to the disk array, and clearly stated prices for SLA and data export. Learn more →
For internet providers
Flow monitoring, data retention, threat intelligence, vulnerability scanning and NIS2 reporting run on a single platform. Stop an attack at your upstream with RTBH, and have the regulator's report pre-filled before you start writing it. Learn more →
For business and public bodies
The platform we build for internet providers also watches a company network: you see the traffic, recognise an attack and have the evidence the Cybersecurity Act asks for. Plus an audit and monitoring of how AI is used. In plain language, with evidence for inspections and for your customers. Learn more →
We show it to you on your own network
Internet providers get a 45-minute online walkthrough of the system. With companies and public bodies we start with a free 30-minute consultation.