
NIS2 for internet service providers
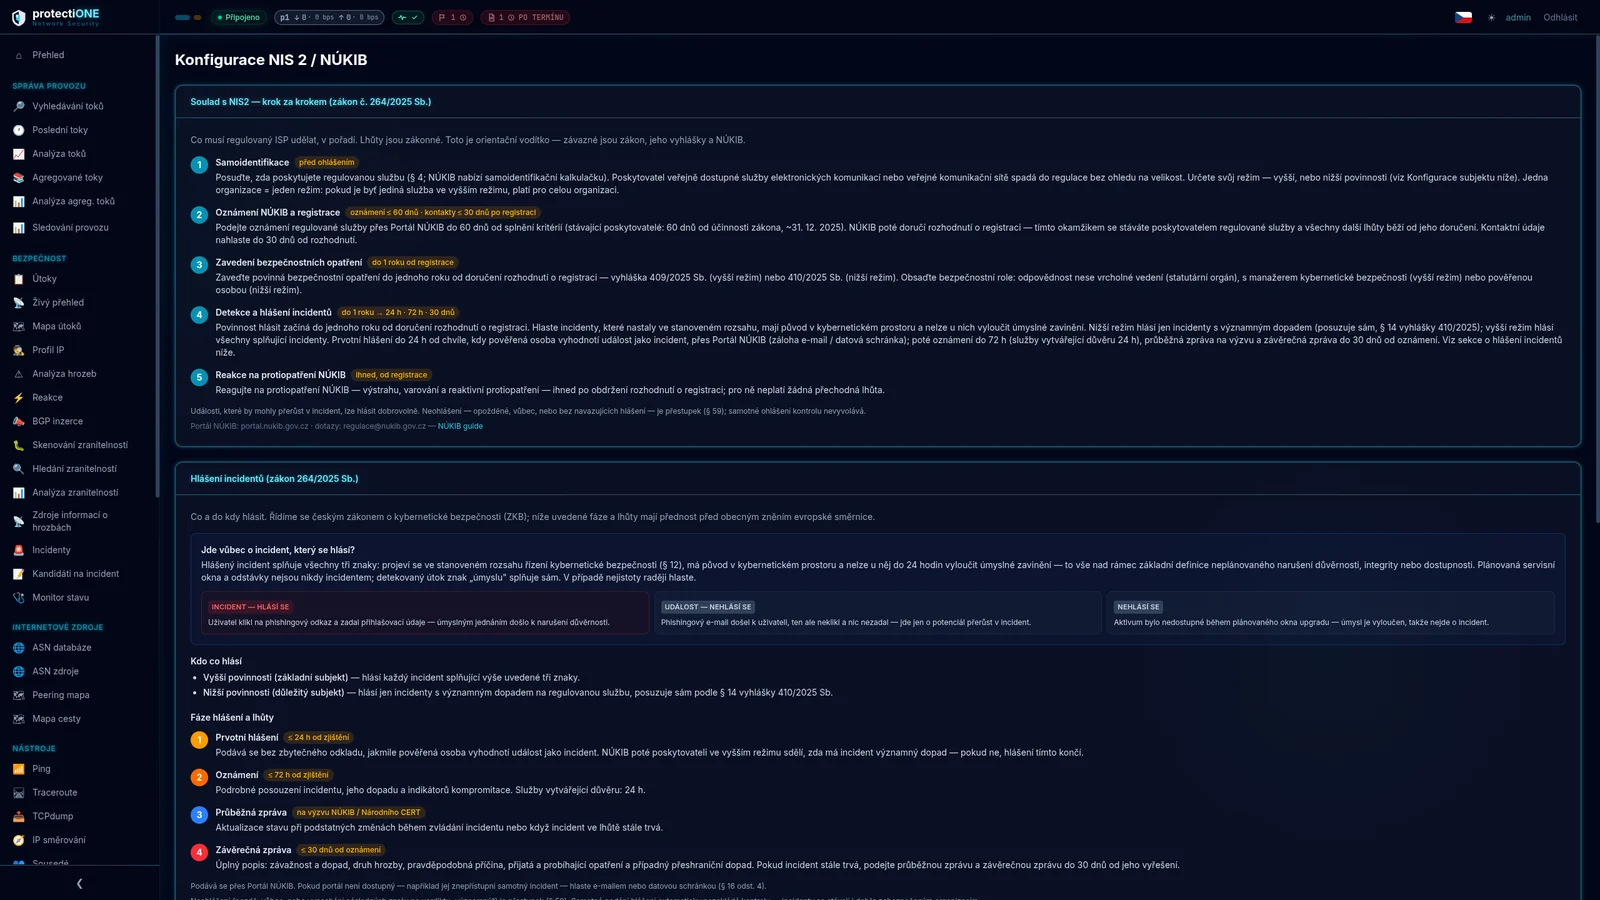
The Czech Cybersecurity Act (No. 264/2025) applies to every ISP regardless of size. The system walks you through what it asks of you – from determining your regime to the final report.
Not a calendar of deadlines. A guide to what the law asks of an ISP.
The module goes beyond the general wording of the directive. It implements the Czech transposition — Act 264/2025 Coll. and decrees 409/2025 and 410/2025 Coll. — in detail. The framework of obligations is the same across the EU; we adapt the module to other national transpositions.
It determines your regime
A provider of a public communications network or service is regulated regardless of size — the small-enterprise exemption does not apply to you. The regime is decided by company size or reach: higher obligations from 350,000 active SIMs or 100,000 fixed connections, otherwise lower obligations. One organisation means one regime.
It decides what even counts as an incident
A reportable incident has three characteristics at once: it occurred within the scope of security management you defined, it originates in cyberspace, and a deliberate cause cannot be ruled out within 24 hours. The system knows these tests and shows you why one outage must be reported and another must not.
It tracks all five stages
Initial report ≤ 24 h · Notification ≤ 72 h (trust services 24 h) · Interim report on the regulator's request · Status report after 30 days if the incident is still open · Final report ≤ 30 days after resolution. For each stage you see how much time is left — or by how much it is overdue.
It knows the rest of the obligations too
Notifying the authority, contact details, security measures within the statutory period, and responding to warnings and reactive countermeasures without delay. Authority contacts, including emergency numbers, sit inside the system, split by your regime.
| Situation | Outcome |
|---|---|
| A user clicked a phishing link and entered credentials | Incident — reportable |
| Phishing arrived but nobody clicked | Event — not reportable |
| Outage during planned maintenance | Not an incident — intent ruled out |
Failing to report — late, not at all, or omitting follow-up reports — is an offence. Reporting an incident does not itself trigger an inspection; incidents happen to well-secured organisations too.
You do not have to guess what is reportable
Health Monitor watches service availability and groups outages into candidate NIS2 incidents on its own — with calculated impact and an assessment of whether the cause looks like a cyber attack.
You then simply decide. Dismiss an operational outage. Promote a real incident into a report that is already pre-filled and carries the evidence: which attacks, from which addresses, at what severity.
Where the system's role ends
The statutory clock starts with your decision — until then the system only flags that there is something to assess. We keep that boundary deliberately: what counts as an incident is decided by your responsible officer, not by software.
Technical solution
The same platform, the same features, the same dashboard. All that differs is where the system runs and who owns the hardware. Learn more →
DDoS protection
The system recognises an attack, names it and can stop it before it fills your link – via RTBH or FlowSpec at your upstream peer. Learn more →
Flow monitoring
Collection from NetFlow v9, IPFIX and port mirroring, with context from the ASN database and global threat sources. All on the same data, on one screen. Learn more →
Data retention
You have to retain traffic and location data anyway. With us, data retention runs on the same data as monitoring and attack detection – one system instead of two. Learn more →
Pricing and SLA
A subscription sized to your network, hardware sized to the disk array, and clearly stated prices for SLA and data export. Learn more →
We show you the system on your network, not on a generic demo
Forty-five minutes, online, no commitment. We go through what the platform would look like at your organisation — how many systems it would replace, how NIS2 reporting would work for you, and what it would mean for your team. Walkthroughs are one-to-one, so the answers are specific rather than generic.