
See every flow – and know at once who it belongs to
Collection from NetFlow v9, IPFIX and port mirroring, with context from the ASN database and global threat sources. All on the same data, on one screen.
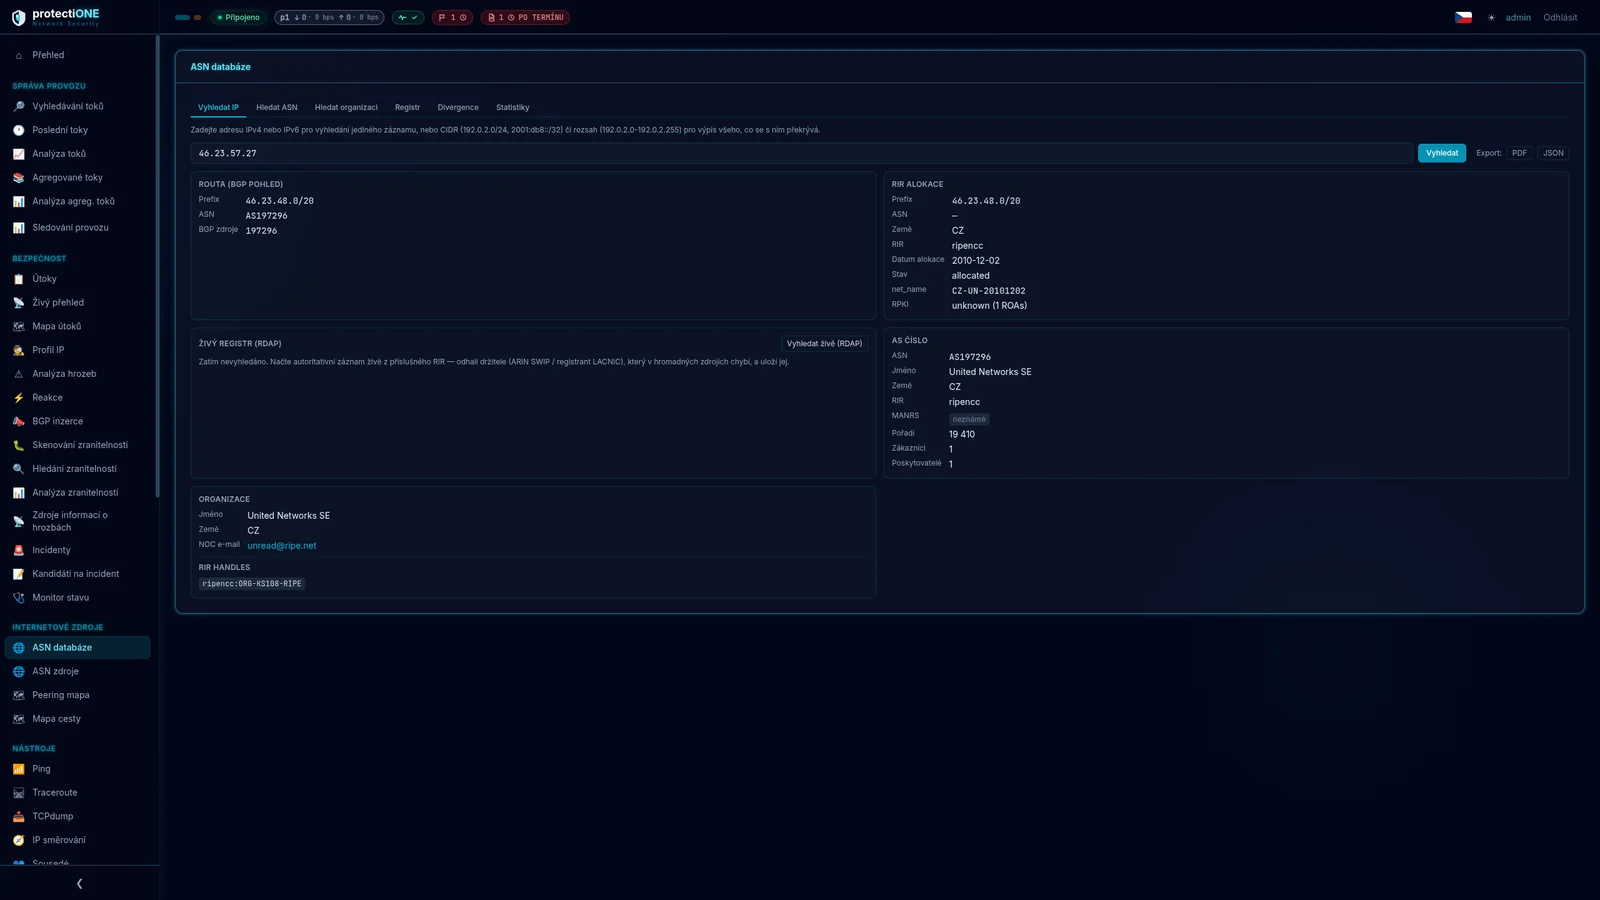
140,315 ASNs, a million routes, refreshed straight from the RIR registries
For any IP address you immediately know who owns it, what its ASN reputation is, how traffic reaches it and what relationships that network has. Data is populated from RIPE NCC (5.0 m records), APNIC (1.2 m), LACNIC, AFRINIC and ARIN over RDAP.
- 140,315 autonomous systems and 486,370 organisations
- 672,532 IPv4 and 430,245 IPv6 routes
- Over 6.9 million address allocation objects
- Beyond a plain lookup: RPKI validation, BCP-38, MANRS, CAIDA rank, Peering Map and Path Map
RPKI and prefix hijack detection
The system continuously compares what is actually announced in global routing against what prefix holders authorised by signing a ROA. A route covered by a ROA that does not authorise the announcing AS is a strong signal of a prefix hijack, a route leak or a configuration error.
- BCP-38 — which networks let spoofed source addresses through
- MANRS — who commits to routing security norms
- Attack Map — interactive map of attack flows with geolocation
- Live Feed — a stream of detected events filtered by severity
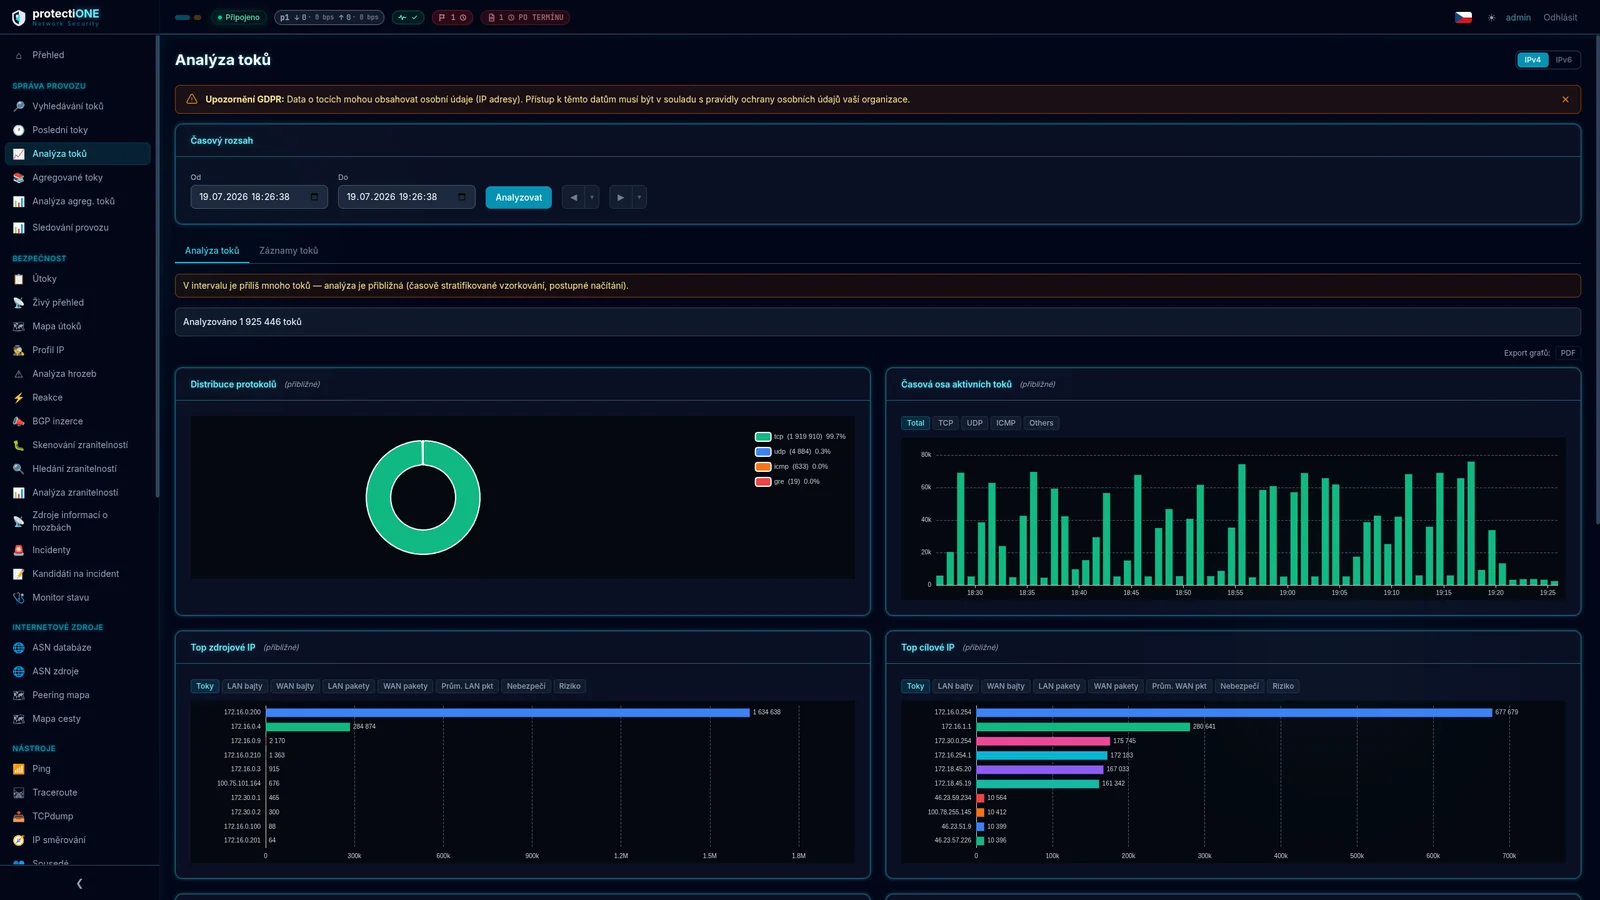
Deep flow inspection
Every IP flow analysed in real time.
Deep flow inspection
Every IP flow analysed in real time.
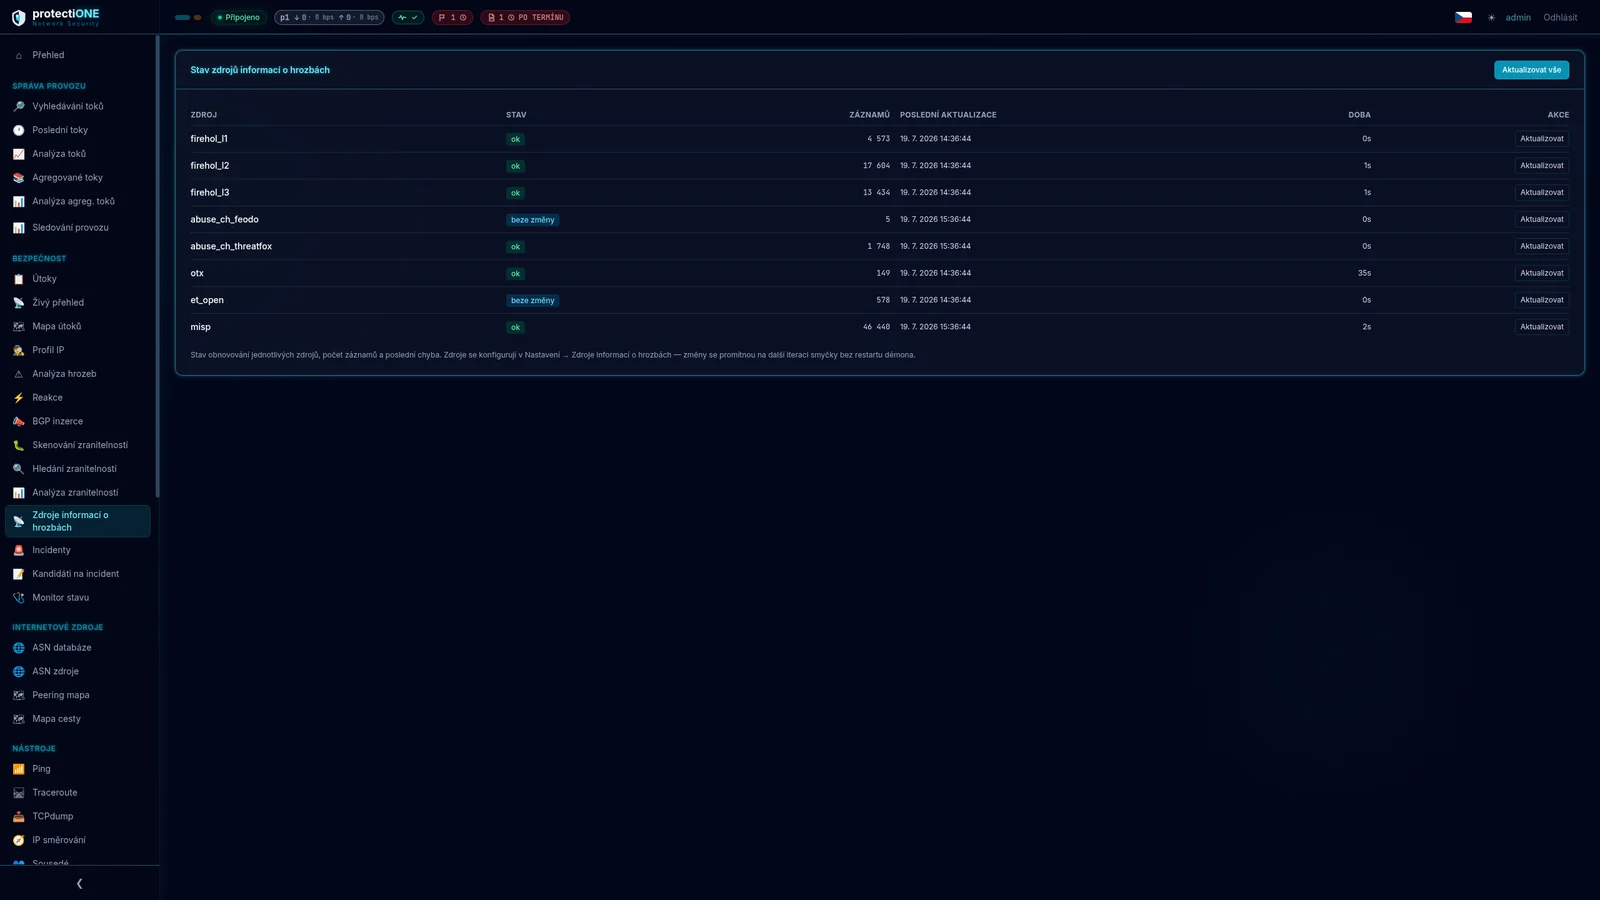
Context from global threat sources
Every flow is enriched with source reputation from eight feeds — FireHOL, abuse.ch Feodo and ThreatFox…
Context from global threat sources
Every flow is enriched with source reputation from eight feeds — FireHOL, abuse.ch Feodo and ThreatFox…
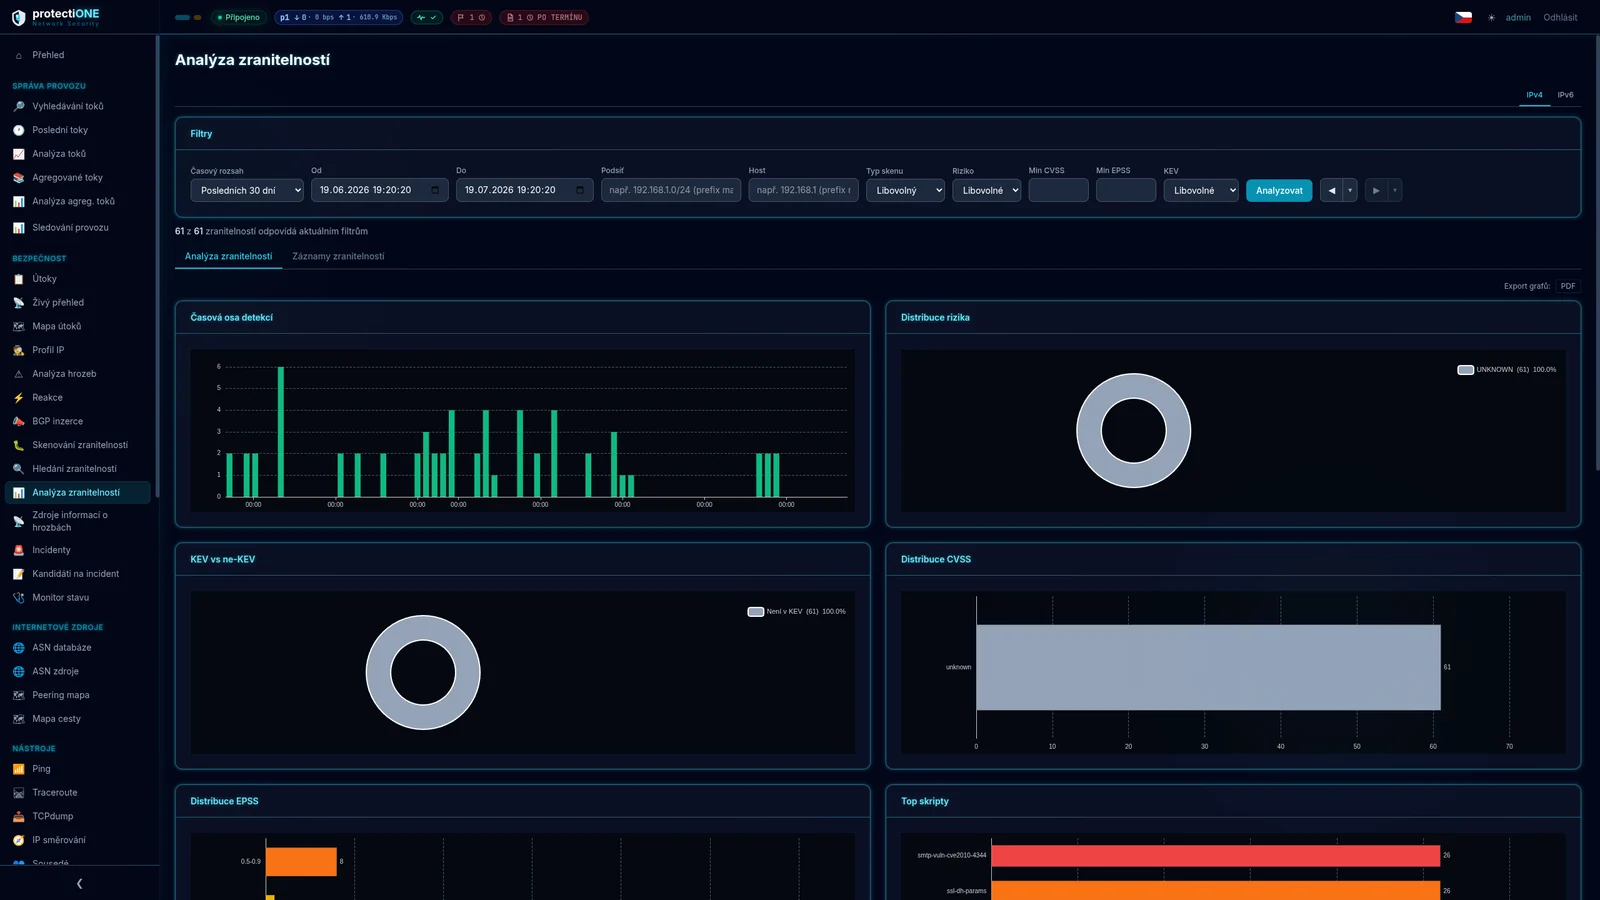
Vulnerability analysis
Vulnerability analysis
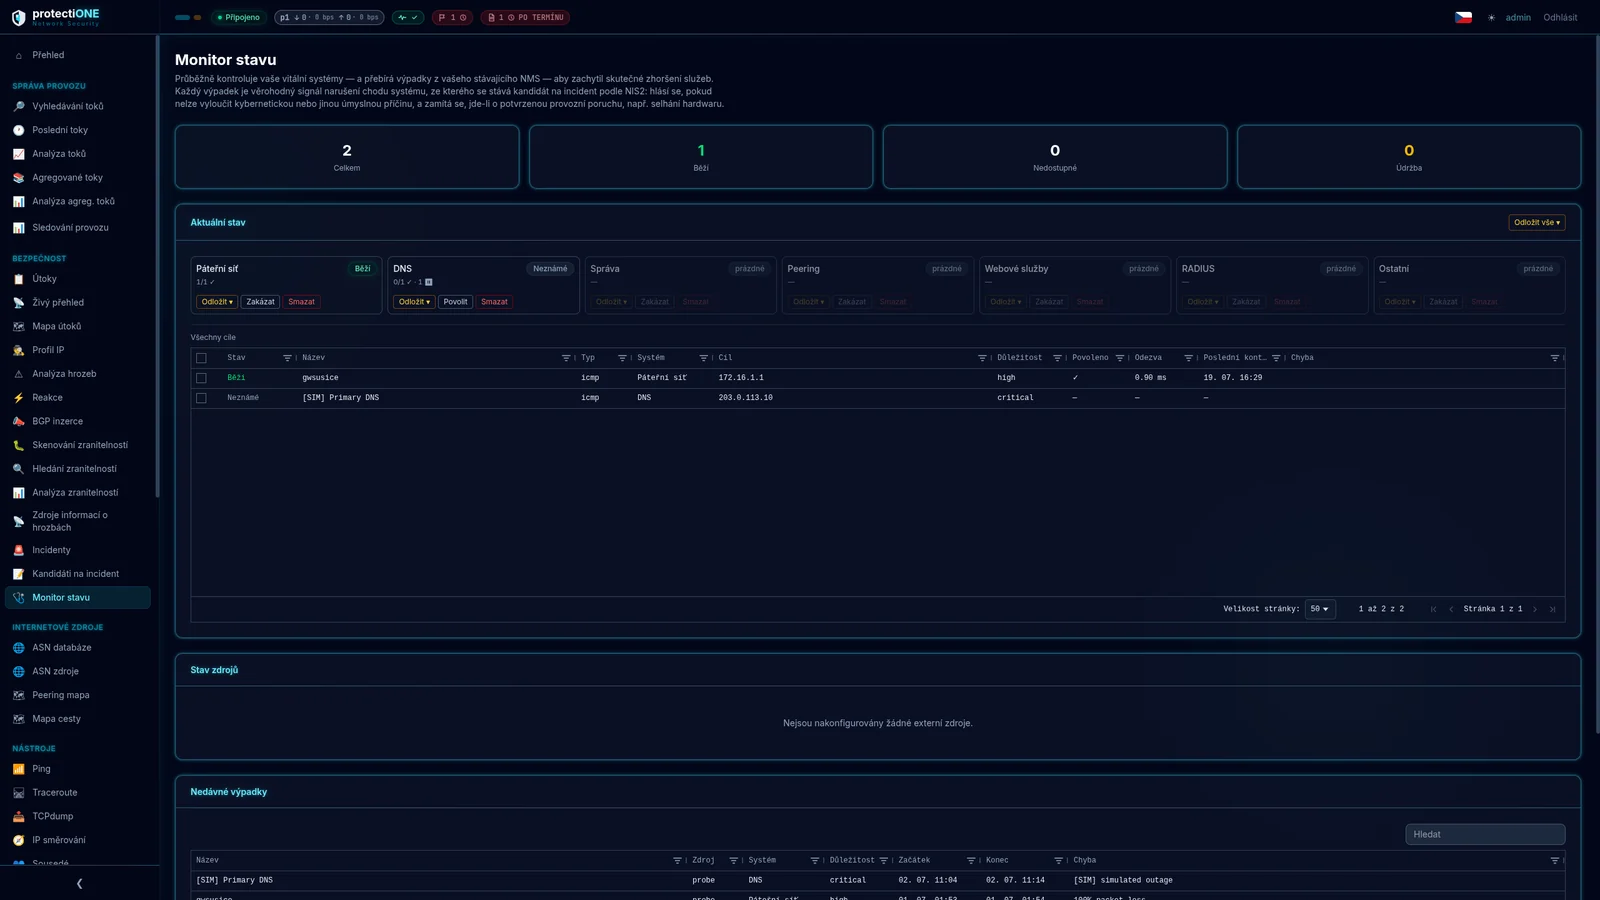
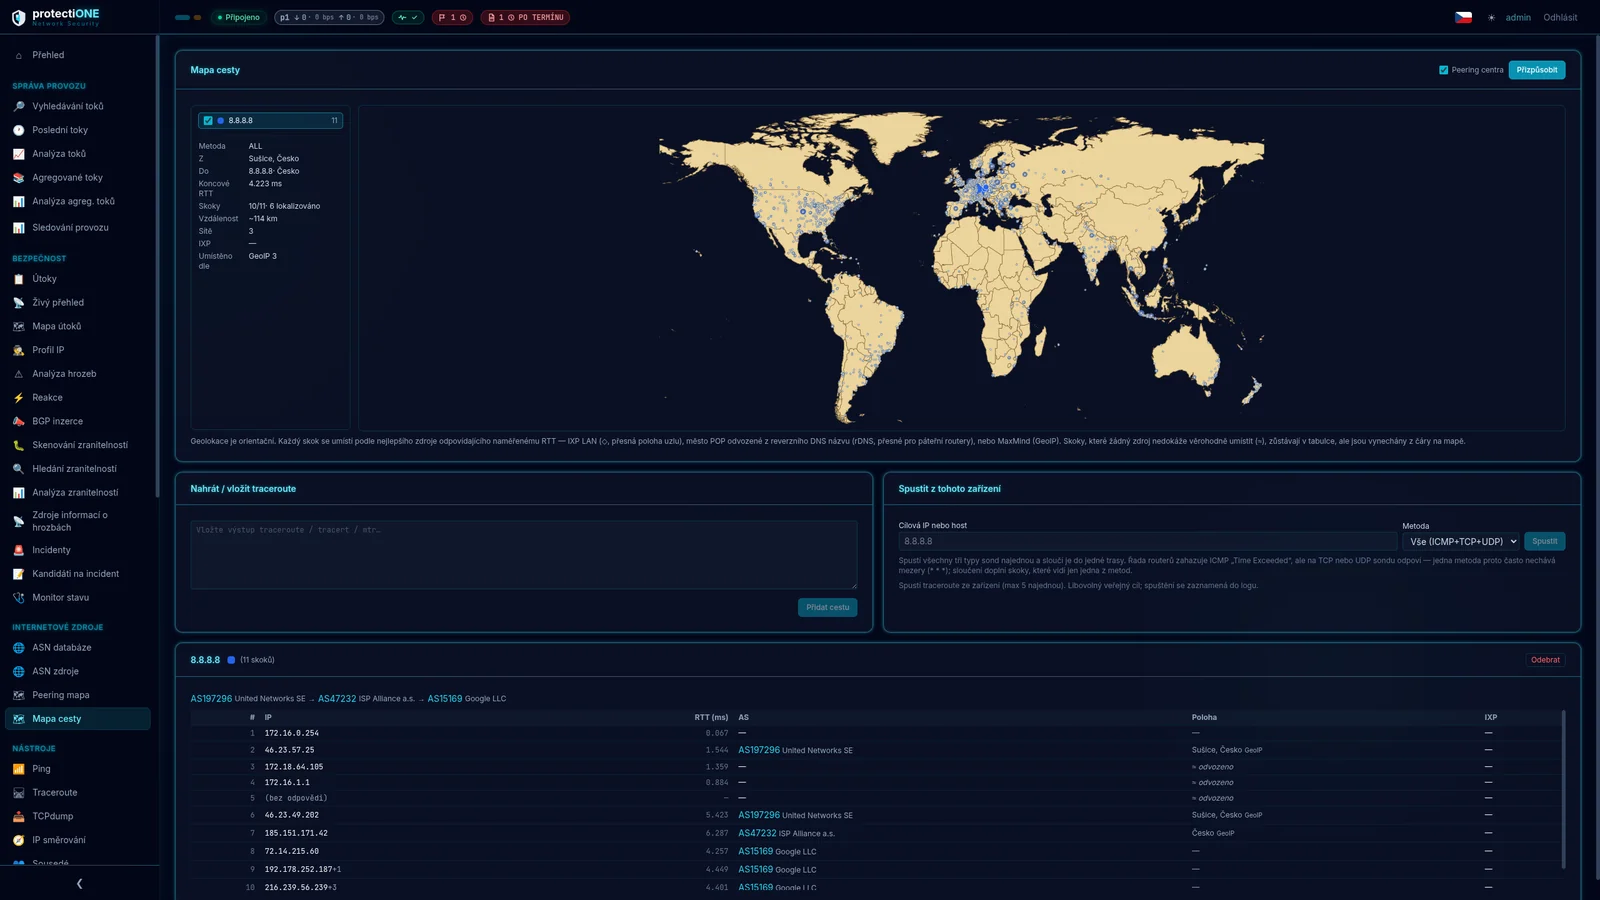
Traceroute where you see the flows
When you are handling an incident at three in the morning, you are not jumping between…
Traceroute where you see the flows
When you are handling an incident at three in the morning, you are not jumping between…
- Ping, traceroute, tcpdump and the routing table built in
- Neighbours, SFP module status, disks and database health
- SMART and IPMI sensors
Technical solution
The same platform, the same features, the same dashboard. All that differs is where the system runs and who owns the hardware. Learn more →
NIS2
The Czech Cybersecurity Act (No. 264/2025) applies to every ISP regardless of size. The system walks you through what it asks of you – from determining your regime to the final report. Learn more →
DDoS protection
The system recognises an attack, names it and can stop it before it fills your link – via RTBH or FlowSpec at your upstream peer. Learn more →
Data retention
You have to retain traffic and location data anyway. With us, data retention runs on the same data as monitoring and attack detection – one system instead of two. Learn more →
Pricing and SLA
A subscription sized to your network, hardware sized to the disk array, and clearly stated prices for SLA and data export. Learn more →
We show you the system on your network, not on a generic demo
Forty-five minutes, online, no commitment. We go through what the platform would look like at your organisation — how many systems it would replace, how NIS2 reporting would work for you, and what it would mean for your team. Walkthroughs are one-to-one, so the answers are specific rather than generic.